Mini PCs
Nano-N1121
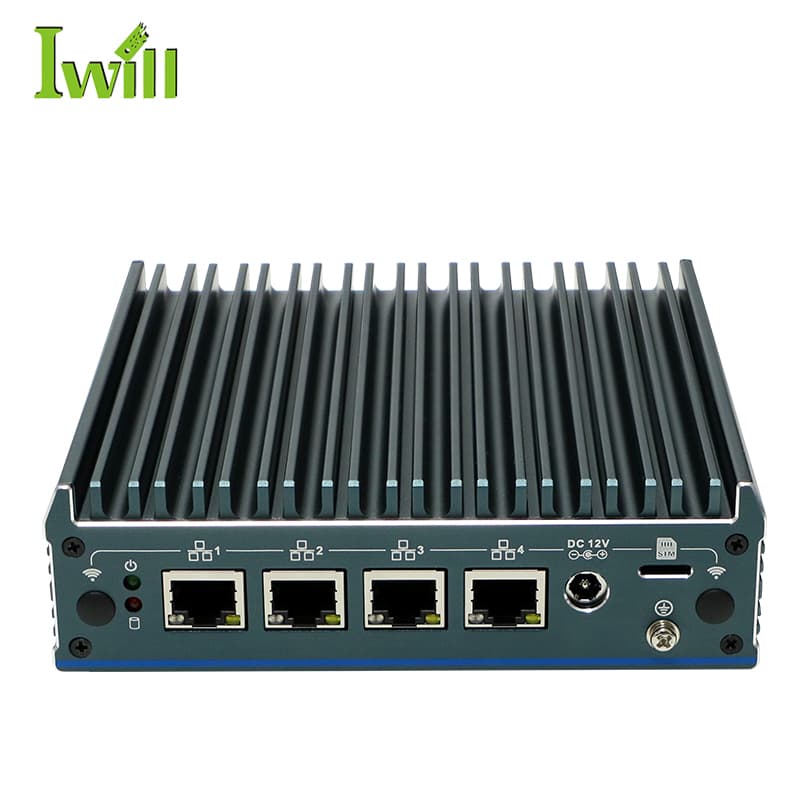
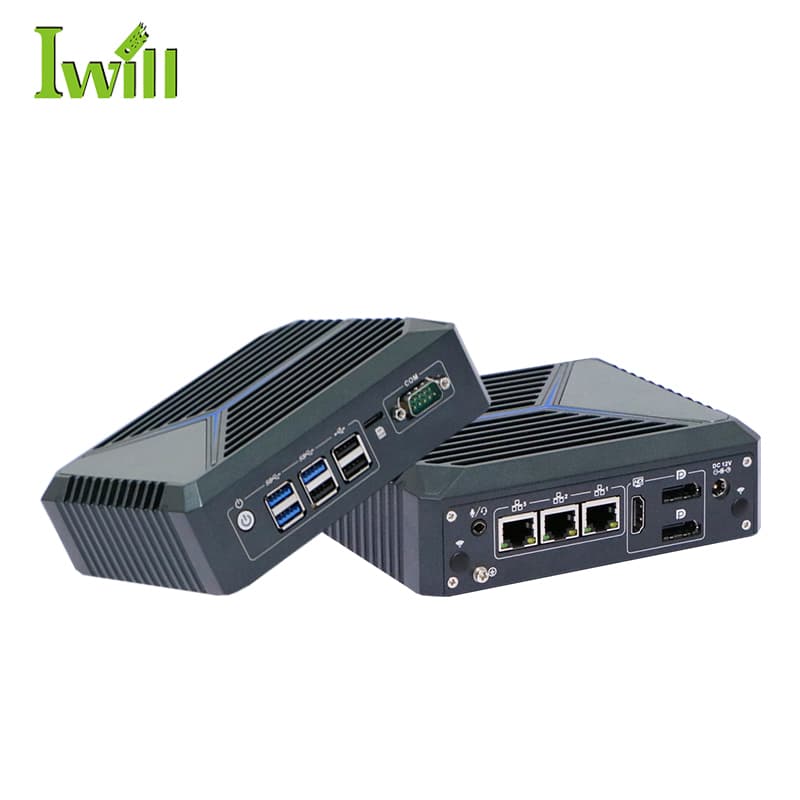
Intel Celeron J6412 (4 cores, 2.0GHz up to 2.6GHz) with 3x 2.5G LAN.
Turnkey firewall appliance
A fanless, silent appliance purpose-built to run pfSense or OPNsense: three 2.5G Intel LAN ports, AES-NI VPN acceleration, and TPM 2.0 — enterprise-grade network security without the enterprise licensing.
The problem
Carrier-supplied routers rarely offer IDS/IPS, a proper VPN server, or VLAN segmentation — and you do not control their firmware.
Many commercial UTM appliances need an annual license to keep security features running. Open-source firewalls do not.
Staff and admins need a secure tunnel into the office or lab that you own and can audit.
Cameras, controllers, and smart devices are easy targets. Isolating them in a separate zone limits the blast radius.
N1121 + pfSense or OPNsense gives you a professional firewall you fully control — no per-feature licensing and no vendor lock-in.
Intel network controllers — the ones the BSD firewall community prefers — for WAN, LAN, and a DMZ or segmentation port at multi-gig speed.
Hardware crypto keeps WireGuard, IPsec, and OpenVPN tunnels at line rate without saturating the CPU.
Passive cooling — no fan, no noise, no dust intake. It disappears onto a shelf or wall bracket.
Hardware root of trust and automatic recovery for an appliance that must simply stay up.
Three physical Intel 2.5G ports cover the classic firewall layout without a managed switch. Add VLAN tagging for more zones.
Port 1
WAN
Connects to the ISP modem or upstream router.
Port 2
LAN
Feeds the internal switch — workstations, servers, Wi-Fi APs.
Port 3
OPT / DMZ
Guest network, DMZ, IoT zone, or a second WAN for failover.
Software compatibility is validated for the exact model and release before quotation.
Both are mature, open-source, FreeBSD-based firewall platforms and both run on this hardware. The choice usually comes down to interface preference, update cadence, and the packages your team already knows.
| Feature | pfSense CE | OPNsense |
|---|---|---|
| Base system | FreeBSD | FreeBSD |
| Interface | Classic, widely documented | Modern, menu-driven |
| VPN | IPsec, OpenVPN; WireGuard via package | IPsec, OpenVPN, WireGuard built in |
| IDS / IPS | Snort or Suricata packages | Suricata built in |
| Release cadence | Fewer, larger releases | Two major releases a year, frequent updates |
| License | Apache 2.0 | BSD 2-Clause |
| Commercial edition | pfSense Plus (Netgate) | Business Edition (Deciso) |
Tell us which platform and release you plan to run; compatibility is confirmed for the exact build before quotation.
How an open-source firewall on your own hardware compares with the two common alternatives. Individual vendor products vary; this is the typical picture.
| Feature | N1121 + pfSense / OPNsense | Subscription UTM appliance | ISP-supplied router |
|---|---|---|---|
| Recurring license | None required | Usually required for security features | None |
| VPN server | WireGuard, IPsec, OpenVPN | IPsec / SSL VPN | Limited or none |
| VLAN segmentation | Yes | Yes | Rarely |
| IDS / IPS | Suricata or Snort (open source) | Vendor engine, subscription | No |
| Vendor lock-in | No — standard x86 hardware | Yes | Yes |
| Firmware control | Full — you choose when to update | Vendor schedule | ISP controlled |
Segmentation, VPN, and content filtering for offices up to gigabit WAN.
A quiet, capable firewall for a rack in the study — Proxmox, VLANs, the works.
Standardized, imaged appliances for repeatable MSP deployments.
Starting points technical sales uses when sizing the N1121. Every build is confirmed against your WAN speed, VPN load, and packages before quotation.
Essentials
Home lab and small office
Office
Offices running IDS/IPS and multiple tunnels
Edge / Lab
Virtualized firewall, failover WAN
The appliance is quoted as a validated hardware configuration; the OS image is confirmed per order. We can advise on pfSense or OPNsense installation and settings — compatibility is validated for the exact model and release.
For gigabit and multi-gig WAN with VPN and filtering, yes. If you run heavy IDS/IPS or need 10G uplinks, step up to a Core-class or rackmount platform — send the workload and we will size it.
Yes — with three physical ports plus VLAN tagging, you can separate WAN, LAN, guest, and DMZ networks. Describe the topology in your enquiry.
Send the configuration, quantity, application, and timing. Technical sales confirms compatibility, lead time, and pricing.
We store your analytics preference locally. Optional analytics loads only with your permission. See our Privacy Policy.