Mini PCs
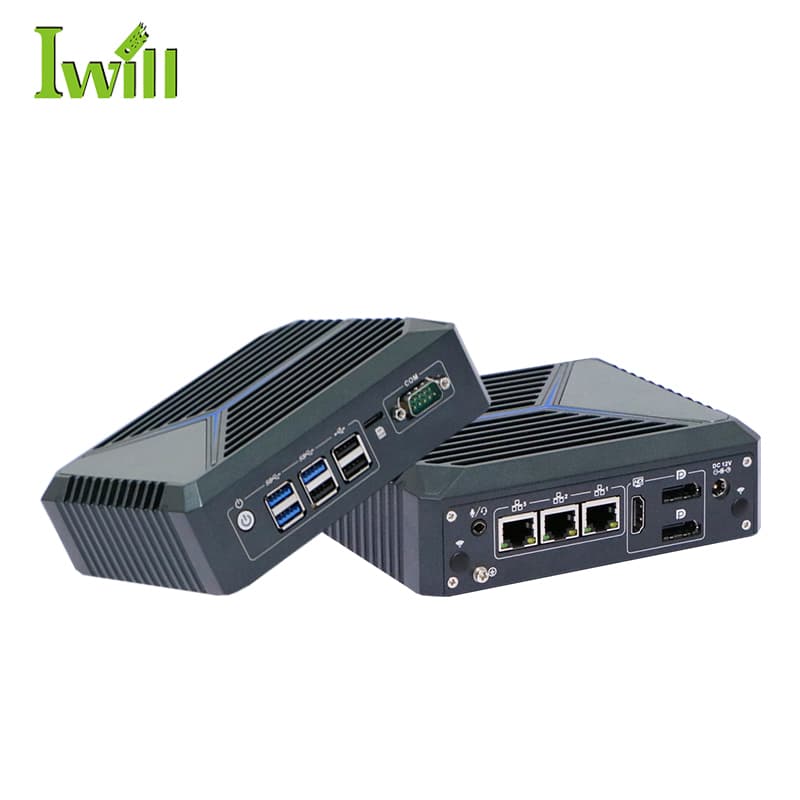
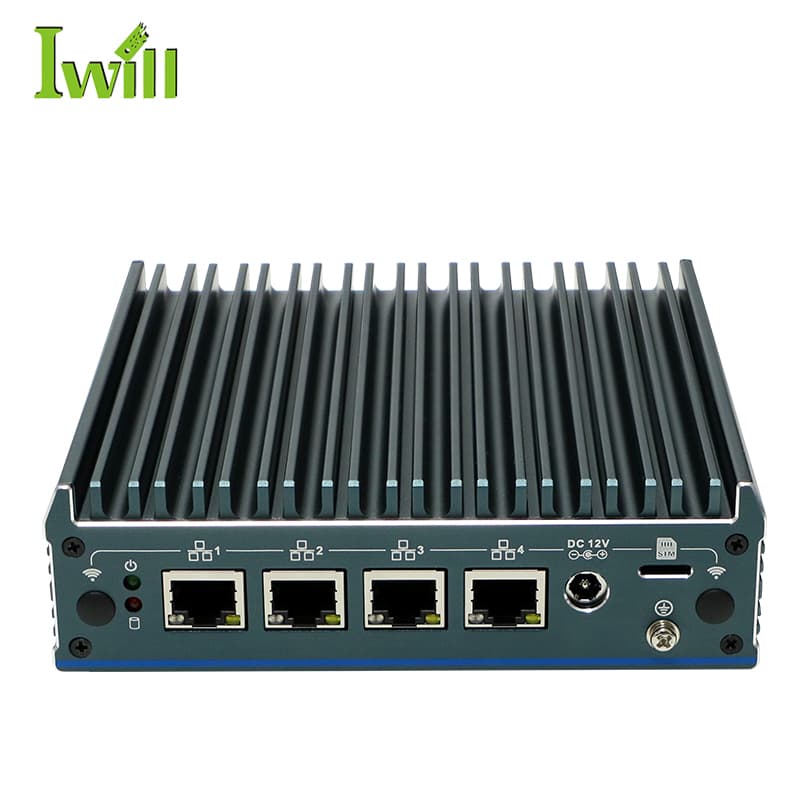
Nano-N1241
Intel Alder Lake N100 (4 cores, up to 3.4GHz) with 4x 2.5G LAN.
AI network isolation
Local models and AI agents make outbound calls and expose services. The N1241 gives them their own network: four 2.5G Intel LAN ports for VLAN zones, egress filtering, and application-aware inspection with OPNsense and Zenarmor.
The problem
Inference servers expose HTTP APIs. On a flat network, every device can reach them — and so can anything that compromises one of those devices.
Tool-using agents browse, fetch, and call APIs by design. Without egress control there is no record of where they went.
Prompt injection and misconfigured tools bypass application-level controls. The network is the backstop.
Security and compliance reviews want to see which system talked to what. Flow-level visibility answers that.
Put the AI stack in its own zone: inbound only where it is needed, outbound only to what it is allowed, and every flow logged.
One physical port per zone — AI hosts, agents, users, management — so isolation is real wires, not just switch config.
Deny-by-default outbound with an allowlist contains what the AI stack can reach, and logs what it tries.
Zenarmor on OPNsense shows which app and destination every flow belongs to — the answer every security review needs.
Alder Lake N100 with AES-NI keeps DPI and VPN at LAN speed, fanless, next to the hosts it protects.
Four physical Intel 2.5G ports give each zone its own wire. VLANs extend the layout when you need more.
Port 1
WAN
Upstream internet or corporate network.
Port 2
AI hosts
Inference servers — inbound only on the API port.
Port 3
Agents
Tool-using agents with allowlisted egress and full logging.
Port 4
Users / management
Staff workstations and the admin interface.
Software compatibility is validated for the exact model and release before quotation.
Both are mature, open-source, FreeBSD-based firewall platforms and both run on this hardware. The choice usually comes down to interface preference, update cadence, and the packages your team already knows.
| Feature | pfSense CE | OPNsense |
|---|---|---|
| Base system | FreeBSD | FreeBSD |
| Interface | Classic, widely documented | Modern, menu-driven |
| VPN | IPsec, OpenVPN; WireGuard via package | IPsec, OpenVPN, WireGuard built in |
| IDS / IPS | Snort or Suricata packages | Suricata built in |
| Release cadence | Fewer, larger releases | Two major releases a year, frequent updates |
| License | Apache 2.0 | BSD 2-Clause |
| Commercial edition | pfSense Plus (Netgate) | Business Edition (Deciso) |
Tell us which platform and release you plan to run; compatibility is confirmed for the exact build before quotation.
Isolate Ollama / LM Studio hosts with inbound only on the API port, outbound denied.
Give agents a zone with allowlisted egress and full logging.
Segment mixed local-model and cloud-API workloads with DPI visibility.
Starting points for sizing the N1241. Zenarmor tier, rule count, and throughput targets are confirmed before quotation.
Lab
Single inference host, home or lab
Team
Small team with agents in production
AI runtimes expose HTTP APIs and make outbound calls by design; on a flat network everything can reach them and they can reach anything. VLAN isolation and egress filtering contain that — the backstop when application guardrails fail.
An application-aware inspection plugin for OPNsense. It classifies traffic by application and destination and enforces policy — the free tier suits home/lab use, commercial tiers add depth.
For small-team LAN speeds with AES-NI, yes. For office-wide IDS/IPS at high throughput, size up to a six-port or rackmount platform.
Send the configuration, quantity, application, and timing. Technical sales confirms compatibility, lead time, and pricing.
We store your analytics preference locally. Optional analytics loads only with your permission. See our Privacy Policy.